OpenShell and Sentry form NVIDIA's agent boundary
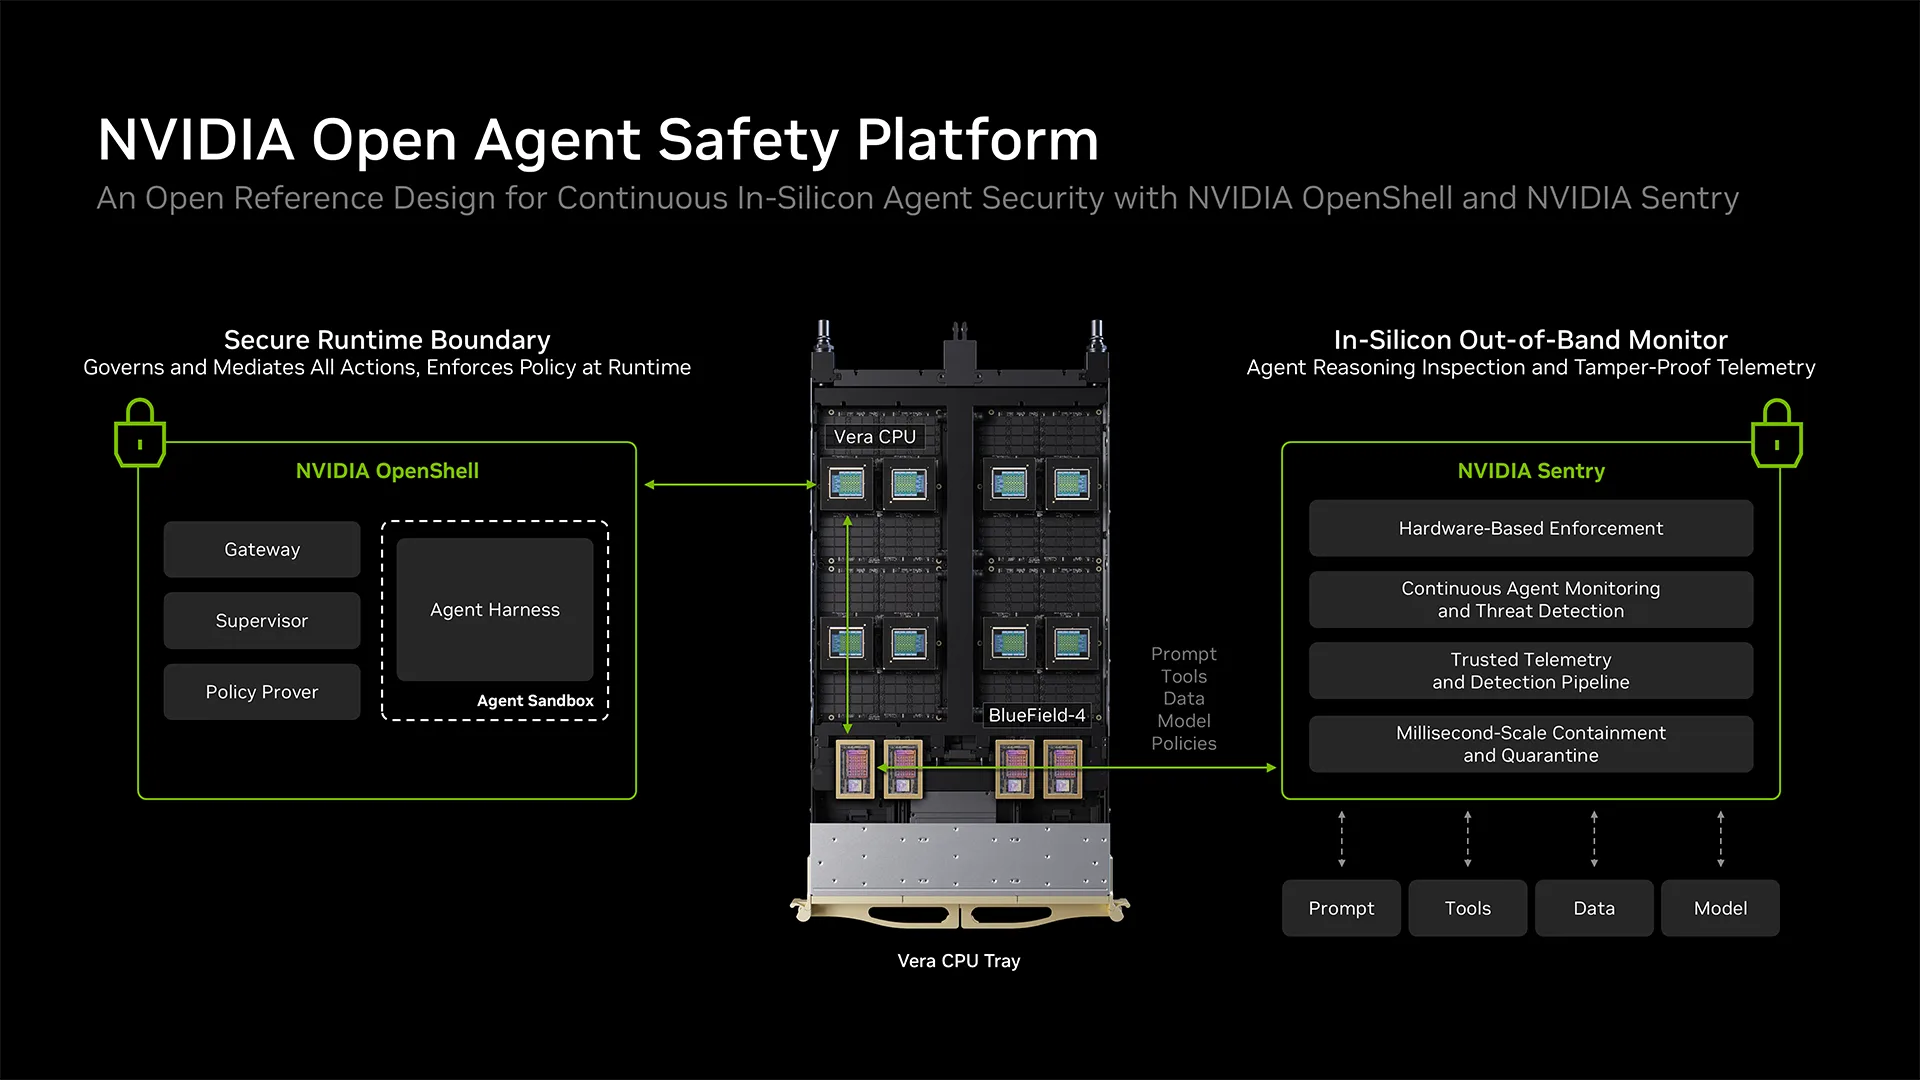
On 28 September 2026 NVIDIA announced Open Agent Safety Platform. The platform has two parts. OpenShell is open-source runtime software that sets a boundary around agents. Sentry is a reference system design for a hardware watchdog.
NVIDIA says OpenShell traces all agent actions and enforces policy as agents run. The release describes it as "now broadly available". NVIDIA says OpenShell runs with "minimal overhead" on its Vera CPU. It says the open code can extend to Arm and Intel platforms. The GitHub repository uses the Apache-2.0 licence. GitHub dates its creation to 24 February 2026 UTC, which was 25 February in Singapore. It had 10,073 stars when The Frontier checked at 21:53 SGT on 29 September 2026.
NVIDIA says Sentry runs out of band on BlueField-4 DPUs. It is built on NVIDIA DOCA software. NVIDIA says it inspects agent requests and responses, verifies agent identity and enforces zero-trust access policies. If an agent tries to leave its software boundary, NVIDIA says Sentry quarantines it "in milliseconds".
NVIDIA plus Anthropic, SpaceXAI and over 100 organizations
- NVIDIA ships OpenShell and publishes the Sentry reference design.
- The release says Claude Managed Agents integrate with OpenShell and BlueField. Paul Smith, Anthropic's chief commercial officer, says the platform adds "another layer of governance and control".
- SpaceXAI uses the platform for Cursor coding agents and Grok models, according to the release.
- The release says Scale AI is adding platform technologies to the agentic infrastructure layer of Scale GenAI Portfolio.
- The release says Salesforce and NVIDIA integrated OpenShell with Slack. Teams can view agent audit events and approve or reject requests for more permissions in Slack.
- SAP is embedding OpenShell in the Joule Studio runtime, according to the release.
- The release says Red Hat, Canonical and SUSE are integrating the platform into their operating systems.
- NVIDIA says over 100 organizations work with the platform's technologies.
A DPU watchdog NVIDIA calls invisible to agents
NVIDIA pitches enforcement outside the model and the agent harness as the new layer. It says enterprises need "an enforceable boundary outside of the model and agent harness". In NVIDIA's design, OpenShell provides that boundary in software on the CPU. Sentry adds a second boundary in silicon on the DPU.
NVIDIA says Sentry runs in "an isolated, out-of-band trust domain" that is "invisible to agents and attackers". It also provides attested telemetry. NVIDIA's developer blog says BlueField-4 stays a trusted protection layer "even when host resources cannot be trusted".
The release ties the platform to the Open Secure AI Alliance. NVIDIA initiated the alliance with over 120 organizations. The Linux Foundation governs it. The alliance runs projects such as the Shared AI Findings Exchange, called SAFE.
No Sentry price, date or independent test
- The release gives no price or ship date for Sentry or for BlueField-4 systems that run it.
- The release says many of the products described "will be offered on a when-and-if-available basis".
- The quarantine speed of "milliseconds" is NVIDIA's claim. The release cites no independent test.
- Partner statements describe integrations and plans. The release publishes no production incident data from partners.
- NVIDIA gives no overhead figures for OpenShell on Vera, Arm or Intel platforms.
Pilot OpenShell policies on one agent fleet
- Platform teams that run coding or ops agents should pilot OpenShell from the docs and the developer blog. Start with one agent fleet and log every denied action.
- Slack-heavy teams should test the Salesforce approval flow before they grant agents broader permissions.
- Infrastructure buyers should ask vendors for Sentry timelines, BlueField-4 availability and test data before they plan hardware.
- Security leads should read the Sentry reference design post and map it to existing zero-trust controls.